PTaaS vs Traditional Pentest vs Bug Bounty
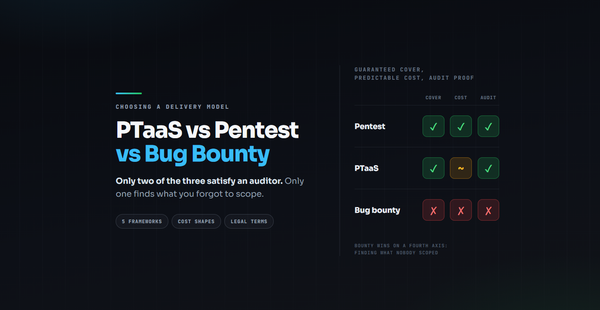
Three ways to buy offensive security, and they are not substitutes. A traditional pentest, a PTaaS subscription and a bug bounty programme buy different things, bill in different shapes, and only some of them satisfy an auditor. Direct answer Which should we buy: a traditional pentest, PTaaS, or a bug